Consider people, groups and links separately
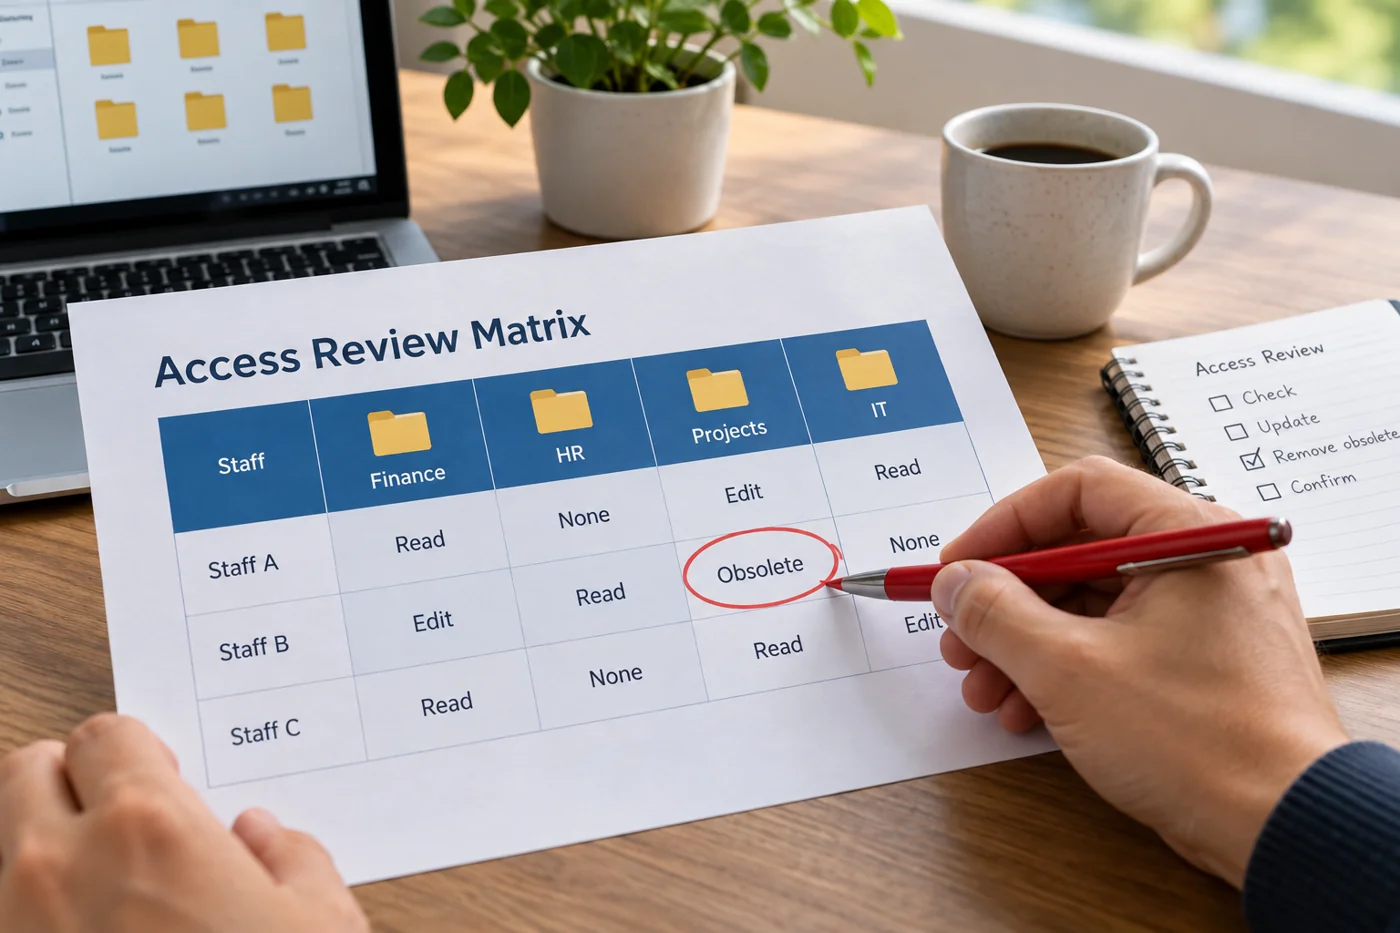
Access may arise through different routes. Check the views available in your application and involve administration where needed. A list of individual names may be incomplete when groups or inherited rights also apply.
Connect each visible permission with a current purpose. Does the person need ongoing editing, occasional reading or no further access? Previous project participation is a reason to investigate, not automatic proof that permission may be removed. Clarify uncertain cases with the responsible people.
Prepare traceable changes
Record the proposed adjustment and reason. Check affected tasks and cover arrangements. Other processes may depend on permissions in a shared folder. Blanket tidying based on names or last contact can therefore have unexpected consequences.
Make changes only with the intended authority and under internal rules. Record what changed and then test necessary access. A successfully saved settings dialog alone does not prove collaboration still works.
Agree recurring triggers
Project completion, role changes and the end of temporary collaboration are useful triggers. A periodic review may supplement them. Frequency should match content and organisational requirements rather than an arbitrary general recommendation.
Keep review results in an appropriately protected location because they may describe people and internal structures. The benefit is a justified current access arrangement. A long table without clear ownership or implemented decisions does not improve the situation. Identify who follows unresolved cases so they do not remain indefinitely in the review merely because nobody has enough context to decide them alone.
Assess access against its working purpose
Review the reason for access as well as the name. Someone may have left the project but still be needed for agreed follow-up work. Conversely, a former role may no longer justify current access. Record uncertain cases for a decision instead of automatically confirming them.
Include groups and shared access routes where these are visible in the system. A list of individual names may not represent everyone who can actually enter the area. When needed, the responsible administrator can explain the technical scope, while the business owner must judge the continuing need.
Apply confirmed changes through the intended procedure and check their effect on active work. Avoid unexpectedly removing access in the middle of a task that remains assigned. Record the reviewed scope and open points so the next review has a starting position. If a permission is retained temporarily, identify the event that should trigger another check rather than letting the exception become indefinite.
For each unresolved point, identify a decision owner and next review date. This keeps the review visibly incomplete instead of incorrectly presenting it as finished.